
AI Agent State Explained: Context, Memory, Sessions, and Checkpoints
AI agent state is the structured information that lets an agent know what is happening, what has already happened, and what should happen next. This guide separates state from context, conversation history, memory, sessions, checkpoints, and logs so you can reason about reliable agents without treating every stored fact as “memory.”
AI Agent State: The Quick Answer
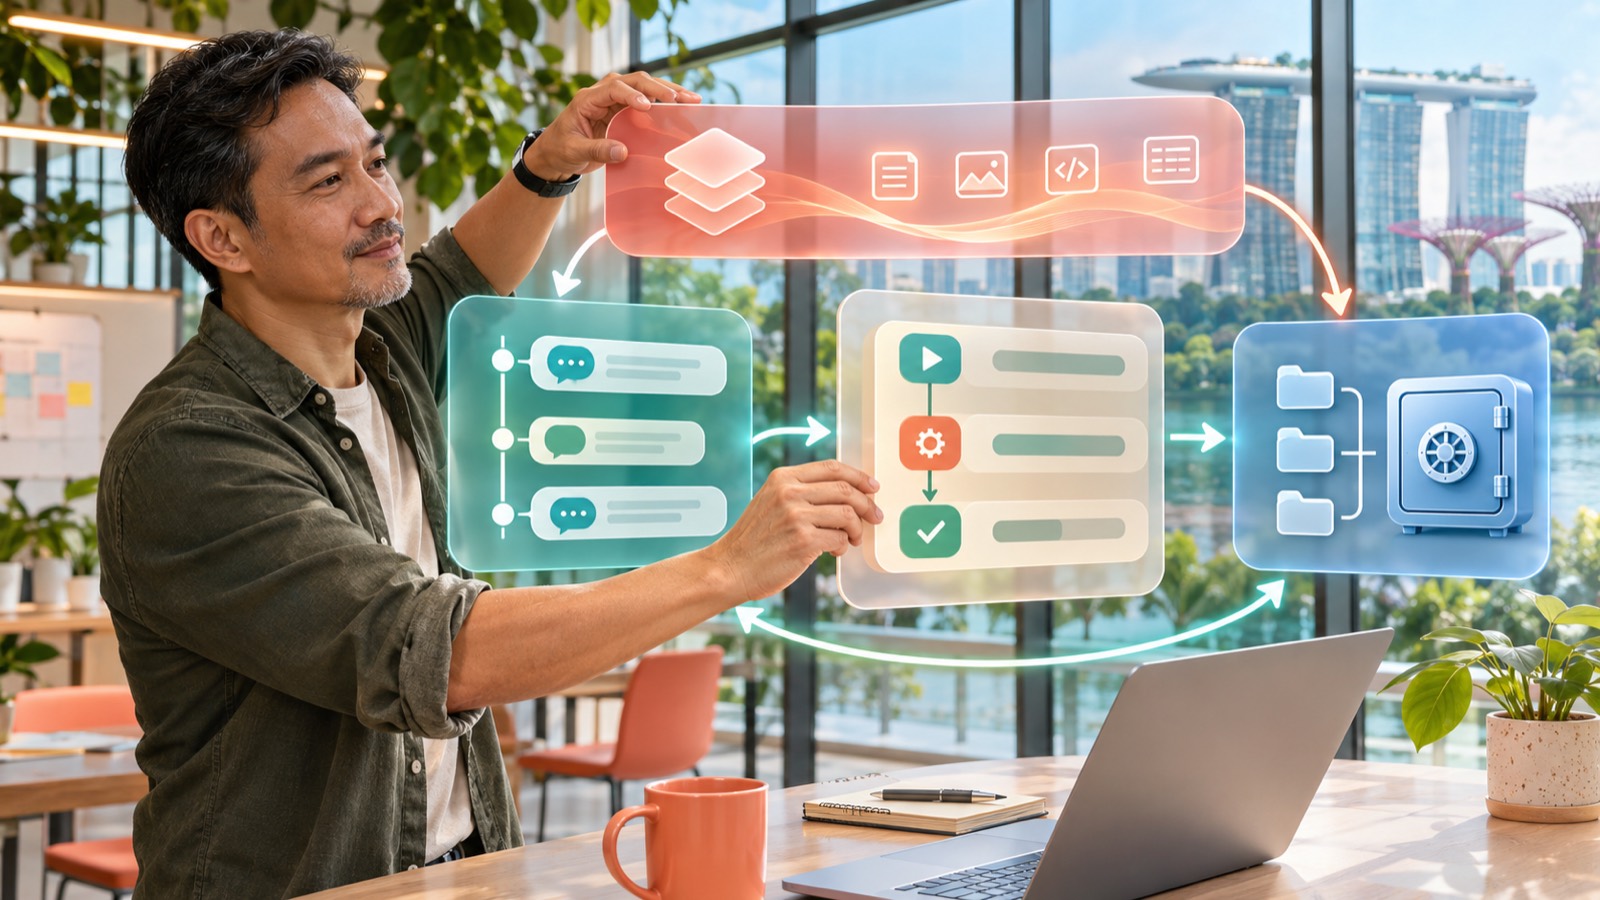
AI agent state is the set of values a system needs to represent the current condition of an agent task. It can include the task identifier, current step, goal, plan, tool results, approval status, pending actions, completed effects, retry count, budget, owner, version, and the evidence needed to continue safely. State answers a practical question: if the process stops now, what must the system know to make the next correct decision?
State is broader than the text visible to a language model. Some state may be rendered into a prompt, but much of it should remain in application code, a workflow engine, a database, or a durable checkpoint. The model does not need to see a database connection, an authorization object, or every historical event to use them correctly. The surrounding agent system can enforce those values while giving the model only the relevant slice.
State is also not a synonym for memory. Memory usually means information retained for later recall, such as a user preference, a project convention, or a useful lesson from an earlier task. Workflow state represents what is true about a particular execution now. A shipping agent may remember that a customer prefers recyclable packaging, while its workflow state records that order 481 is validated, payment is authorized, shipment creation is pending, and a human approval expires at 17:00.
This distinction matters because different information needs different lifetimes, owners, security rules, and recovery behavior. Conversation history may last for one session. A tool result may matter for one step. A payment receipt may need durable retention. A user preference may persist across many tasks. An audit event may be immutable even after the workflow is complete. Putting all of these into one transcript or vector database creates confusion, stale instructions, privacy exposure, and unreliable recovery.
The Seven-Layer Map of AI Agent Information
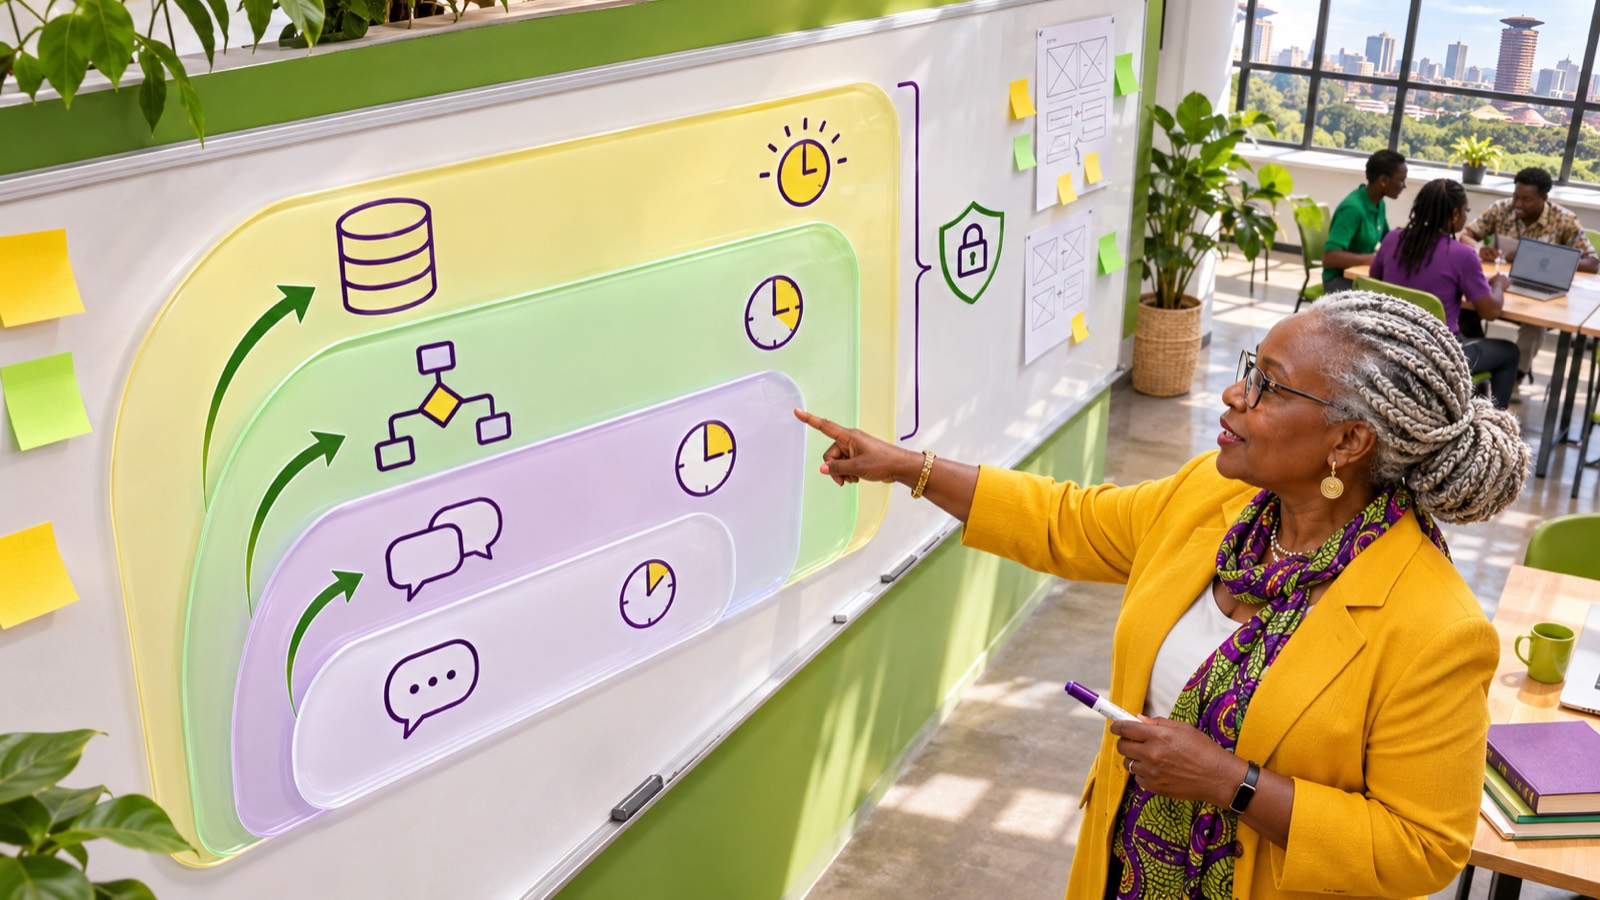
People often describe an agent as if it has one container called memory. Production systems usually need several stores with different purposes. The names vary across frameworks, but the underlying questions remain stable: who owns the information, how long should it live, who may change it, and what happens if it is missing?
| Layer | Main purpose | Typical lifetime | Example | Primary owner |
|---|---|---|---|---|
| Model context | Information available to the model for the current inference | One model call | Instructions, selected messages, retrieved passages, current tool result | Agent runtime |
| Conversation history | Continuity across turns in one interaction | One session or thread | User messages, assistant responses, tool-call items | Session service |
| Application context | Local dependencies and request-scoped data used by code | One run or request | User ID, database client, policy evaluator, logger | Application |
| Workflow state | Current operational condition of a task | One task or workflow | Current node, plan version, approvals, pending action, effect ledger | Workflow engine |
| Checkpoint | Restorable snapshot at a known boundary | Until recovery is no longer needed | Serialized state after validation and before an external write | Durable runtime |
| Long-term memory | Reusable information across tasks or sessions | Days to months, subject to policy | Preferences, project facts, reusable lessons | Memory service |
| Audit history | Evidence of decisions and effects | Policy-defined retention | Who approved, what tool ran, what changed, which policy applied | Independent evidence system |
The table is not a demand for seven databases. A small application may store several layers in one database while keeping separate schemas, access rules, and retention policies. The important boundary is conceptual. Conversation history should not silently become authorization. Long-term memory should not replace the current source of truth. A checkpoint should not be mistaken for an audit record. An audit log may prove what happened without containing everything needed to resume.
Why lifetimes are more useful than labels
Framework vocabulary changes quickly. One product may call conversation history “memory,” another may call it a “session,” and another may expose server-managed conversation state. Instead of arguing about labels, ask four questions. Does the information need to survive the current model call? Does it need to survive a process restart? Should it be available to another task? Must it remain as evidence after the task ends? The answers reveal the correct layer.
The official OpenAI Agents SDK context guide explicitly separates local application context from the information visible to the model. Its sessions documentation describes conversation history stored for continuity across runs. The SDK's sandbox memory guidance separately describes lessons distilled for future runs. These mechanisms solve related but different problems.
State vs Context vs Memory vs Sessions vs Checkpoints
State vs context
Context is an input view. State is the underlying condition. A model might see a sentence saying, “The refund is awaiting manager approval.” The workflow state may hold a structured approval record with an approval ID, requester, amount, policy version, expiry time, reviewer role, and status. The sentence helps the model reason. The structured record controls what the system may do.
Context must be selected because model windows are finite and irrelevant information can distract reasoning. State should be complete enough for the application to enforce invariants. If a crucial approval exists only in model context, a later compaction or handoff may lose it. If every state field is dumped into the prompt, the model receives noise and potentially sensitive data. Good context engineering renders the smallest trustworthy view of the state needed for the next decision.
State vs conversation history
Conversation history records what participants said and what interaction items occurred. It is useful for continuity, tone, corrections, and references such as “use the second option.” It is not automatically a reliable representation of task progress. A transcript may say that a file was uploaded, while the upload actually failed. It may contain a proposed plan that was later rejected. It may omit an external action completed by another service.
Derived workflow state should therefore be grounded in verified events, not merely the latest message. An agent can use the conversation as evidence, but the application should confirm external facts through authoritative systems. The current order status belongs in the order system. The current deployment belongs in the platform API. The current branch state belongs in version control. A transcript is not the source of truth simply because the model can read it.
State vs long-term memory
Long-term memory helps future tasks start with relevant background. It may store a preference, recurring constraint, project map, or lesson. Workflow state is task-specific and often changes rapidly. Mixing them creates two common hazards. First, temporary facts become permanent. Second, old task instructions return as if they were current authority.
Suppose a user says, “For this one report, exclude European accounts.” That is workflow state or session context, not a global preference. Saving it as long-term memory could corrupt future reports. Conversely, “Use ISO dates in every report” may be a stable preference worth retaining. A memory write should have scope, source, timestamp, confidence, retention, and a way to correct or delete it.
State vs session
A session is usually a continuity boundary and a lookup key. It groups conversation items or related interactions. State is the data being managed. One session may contain several tasks. One long-running task may span several sessions. Treating them as identical makes ownership and recovery unclear.
For a customer-support chat, session history may be enough to answer follow-up questions. For a multi-day procurement workflow, the task needs a separate durable identity, current step, approvals, receipts, and version. The person can open a new chat tomorrow, but the procurement task should resume from its task record, not from a guess based on the last few messages.
State vs checkpoint
A checkpoint is a saved representation of state at a particular boundary. State is the living object; the checkpoint is a restorable snapshot or durable marker. Not every state update deserves a checkpoint. Useful boundaries occur after validation, before an irreversible effect, after a confirmed effect, before waiting for human input, and before handing work to another process.
Microsoft's official Agent Framework checkpoint documentation distinguishes in-memory, file-based, and durable distributed storage. That choice is not cosmetic. An in-memory checkpoint can help a test resume inside one process, but it cannot recover after the machine fails. Durability must match the failure you intend to survive.
How State Moves Through an Agent Run
A reliable agent run is a sequence of controlled state transitions, not just a loop that appends messages. The model may propose the next action, but the application should own the transition. A simple lifecycle makes the separation concrete.
Create a task identity
Assign a stable task ID, owner, goal version, data scope, authority scope, and initial status. Do not use a human-readable title as the only key. The task identity should remain stable across retries, worker restarts, and session changes.
Load authoritative state
Read the latest version from a trusted store. Confirm that the task is still active, the user is authorized, approvals remain valid, and no other worker already owns the lease. Do not rebuild critical state solely from an old prompt or cached transcript.
Render model context
Select the instructions, recent conversation, relevant memory, current state summary, and evidence needed for the next decision. Label untrusted content as data. Omit secrets and internal fields the model does not need.
Validate the proposed transition
Check schema, policy, permissions, budget, preconditions, and expected state version. The model can propose “send invoice,” but code should verify the recipient, amount, approval, duplicate key, and task status before the tool is exposed or called.
Record intent before an effect
For a meaningful external write, persist an intent record with a stable operation key. This creates evidence that the system planned the action and makes ambiguous outcomes easier to reconcile. It also supports the idempotency practices explained in our AI agent idempotency guide.
Execute, verify, and advance
Call the tool, capture its result, then verify the external system. Update the effect ledger and workflow state atomically where possible. If the call times out, do not assume failure and repeat blindly. Reconcile by operation key or query the source of truth.
Checkpoint at a meaningful boundary
Save enough data to resume without replaying unsafe work. Include schema version, step, decisions, confirmed effects, pending work, approval references, and the version of relevant policies. Encrypt sensitive data and restrict checkpoint access.
Close or expire cleanly
Mark the terminal outcome, release leases, revoke temporary authority, retain evidence according to policy, and delete transient state that no longer has a purpose. Completion is a state transition, not simply the moment when the model emits a final answer.
What Goes Wrong When State Is Poorly Designed
The transcript becomes the database
The easiest prototype stores everything in messages. It feels convenient because the model can read its history. Over time, the transcript accumulates stale plans, contradictory results, duplicated tool outputs, and sensitive values. Compaction removes details unpredictably. A later model call then infers operational truth from prose. This is fragile even when the prose is accurate.
Use the transcript for conversational continuity. Store business facts, workflow progress, approvals, and effects in structured systems with explicit versions. Render a concise state summary back into context when needed.
Memory becomes hidden authority
A remembered instruction can influence future behavior without the user seeing it. If memory says a vendor is approved, is that a preference, an old fact, or current authorization? If the agent cannot answer, the memory is too powerful. Long-term memory should inform decisions, not silently grant permissions or override live policy.
A retry repeats a side effect
An agent submits a shipment request, but the network response disappears. The stored state still says “shipment pending,” so a restarted worker submits again. The result is two shipments. This is not primarily a model error. The state model lacks an intent record, a stable operation key, and an external reconciliation step.
Two workers advance the same task
Distributed agents can read the same version and both decide to act. Without optimistic concurrency, a lease, or a compare-and-swap update, both may send messages or change records. A version field is simple but important. Every transition should state which prior version it expects.
A checkpoint restores the wrong world
A checkpoint can restore internal variables, but it cannot reverse time outside the process. If a payment completed after the checkpoint, resuming from that snapshot may repeat the charge. Recovery must reconcile external effects before continuing. The article on AI agent checkpointing explains this safe-resume problem in implementation detail.
Old state poisons a new task
State leaks across tenants, projects, or users when identifiers are weak or caches are reused. The result may be a privacy breach, an irrelevant instruction, or a tool call against the wrong account. Every store needs explicit subject, tenant, task, and environment boundaries. A session ID is not proof that a caller may access that session.
The audit trail cannot reconstruct a decision
A log may show that a tool ran but omit which goal, policy, model context, approval, or state version informed the action. That is activity logging, not decision evidence. For material effects, preserve the minimum chain needed to answer who requested the action, what the system knew, what rule applied, who approved, what changed, and how the outcome was verified.
A Practical State Design Framework
You do not need a complex platform to improve agent state. Begin with a state contract. Define the fields, owners, transitions, invariants, retention, and recovery rules before choosing a database or framework.
Use typed transitions, not free-form updates
Avoid allowing the model to rewrite the entire state object. Define operations such as approve_action, record_effect, pause_for_review, and complete_task. Validate their inputs and preconditions. A typed transition narrows what can change and creates a useful event vocabulary.
Separate observed facts from model interpretations
“API returned status 200 with receipt X” is an observation. “The customer is satisfied” is an interpretation unless supported by evidence. Store provenance and confidence where interpretation matters. Do not let a model-generated summary overwrite the raw tool result or authoritative field.
Version schemas and policies
Long-running tasks may outlive a deployment. A checkpoint created under schema version 3 may not load safely under version 5. Store the schema version and provide tested migrations. Also record the policy version that approved a material action. Current policy may differ when investigators review the event later.
Minimize and expire
Keeping everything forever is not reliability. It increases breach impact, retrieval noise, and the chance that stale information will influence new work. Give each field a purpose and retention rule. Delete scratch state when the task ends. Preserve required evidence separately. Let users correct or remove long-term memory where appropriate.
Protect integrity and confidentiality
State stores may contain prompts, personal data, credentials, tool results, and approvals. Apply encryption, access control, tenant isolation, integrity checks, backups, and redaction. The OpenAI Agents SDK documentation notes that a session identifier selects history but does not authenticate a user. Applications must authorize access to session data and protect the underlying store.
Test state transitions under failure
Kill the worker after writing intent but before receiving a tool response. Restart during human approval. Deliver the same event twice. Load an old checkpoint. Race two workers. Change a schema. Revoke permission while a task is waiting. A system that works only on the happy path does not have durable state; it has a demo.
- Every task has a stable identity and explicit owner.
- Critical state lives outside the model transcript.
- Conversation history cannot grant authority by itself.
- External effects have stable operation keys and verification.
- Transitions check an expected state version.
- Checkpoints match the failures they must survive.
- Resume logic reconciles the outside world before replay.
- Long-term memory is scoped, sourced, editable, and expirable.
- Audit evidence is independent from agent-controlled state.
- Sensitive state has access control, encryption, and retention rules.
Interactive Helper: Where Should This Information Live?
Choose the information's purpose and lifetime. The helper gives a starting recommendation, not a substitute for security, legal, or architecture review.
The most important branch is impact. A remembered color preference can safely improve relevance. A remembered approval cannot safely authorize a payment. High-impact facts need current verification, explicit ownership, and deterministic enforcement even if the model also sees a friendly summary.
Four Practical Examples
1. A support agent handles a refund
The model context contains the customer's request, relevant policy excerpt, and a concise account summary. The conversation session preserves follow-up turns. Workflow state holds the case ID, validated purchase, refund amount, approval status, and current step. A checkpoint is created before waiting for a manager. Long-term memory might hold the customer's communication preference, but not the approval. The audit system records the reviewer, policy version, refund receipt, and final verification.
This arrangement prevents a common error: a sentence such as “manager approved” in the chat cannot trigger payment unless the structured approval record is valid and belongs to the same case.
2. A coding agent resumes after a crash
The conversation describes the bug and constraints. Application context holds the repository client and test runner. Workflow state records the branch, base commit, changed files, test status, and current plan step. The checkpoint contains enough information to reopen the workspace and continue. Version control remains the source of truth for file state. Long-term memory may retain a project convention such as the required test command.
On resume, the agent checks the repository instead of trusting its old summary. If the branch changed while it was offline, the system pauses or reconciles. This is more reliable than asking the model to “continue where you left off” from a compressed transcript.
3. A logistics agent survives an ambiguous tool result
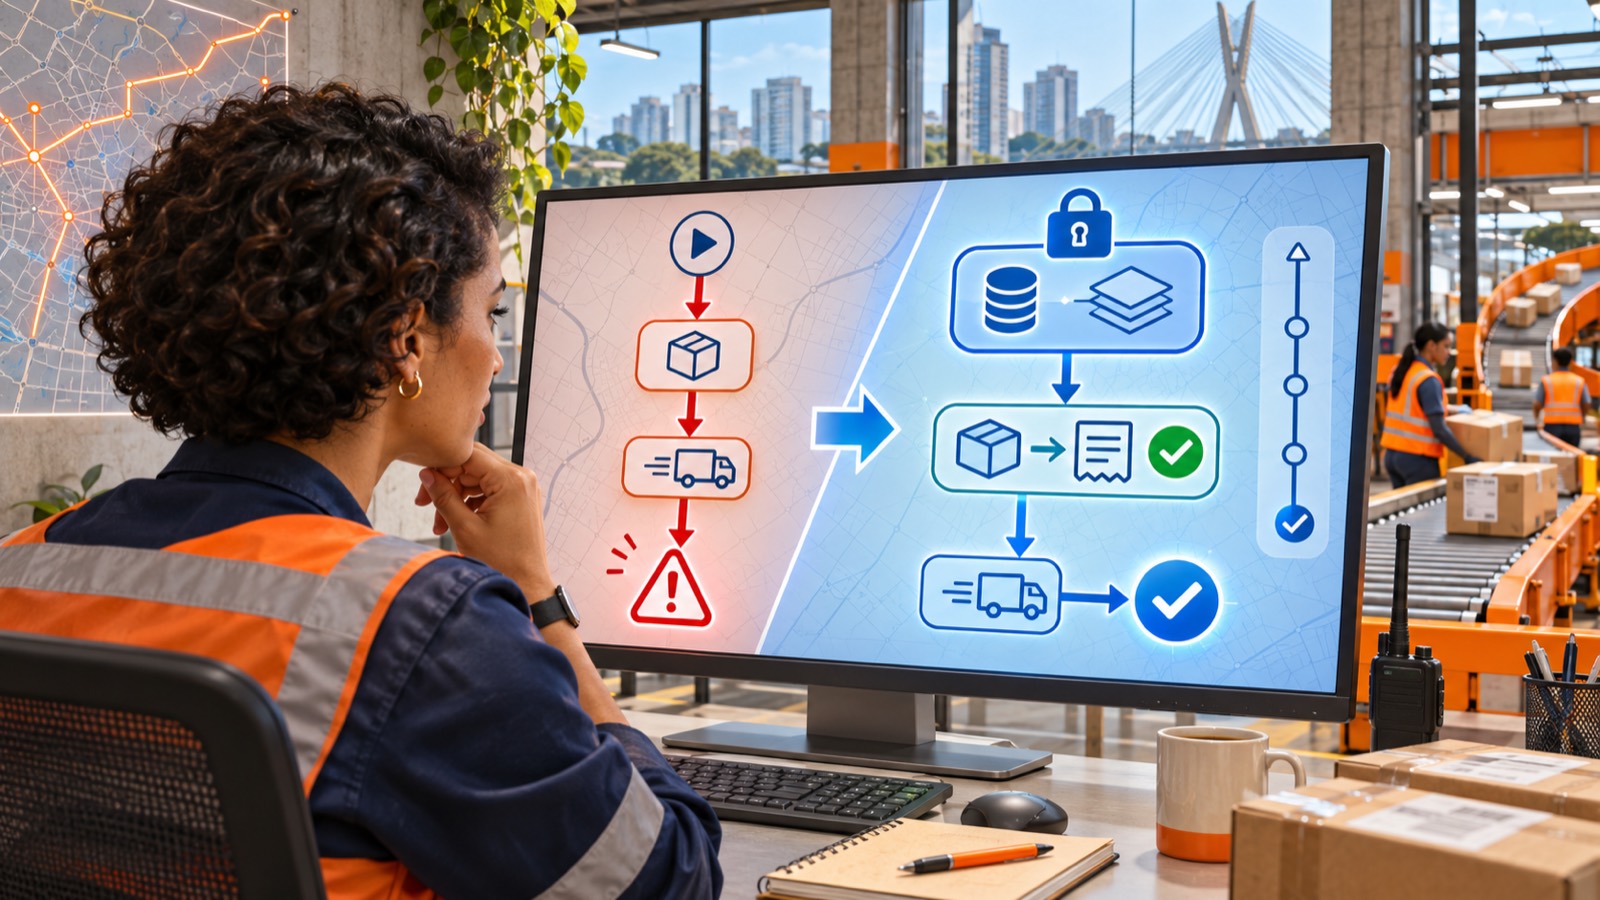
Before creating a shipment, the runtime writes an intent record with a stable operation key. The carrier API times out. The workflow state becomes “outcome unknown,” not “failed.” After restart, the agent queries the carrier using the operation key. If a shipment exists, it records the receipt and advances. If none exists, policy may allow a retry using the same key. The checkpoint helps restore the process, while reconciliation prevents a duplicate real-world effect.
This example shows why checkpointing is not enough. A snapshot can tell the system what it believed before the call. Only the external source of truth can reveal what actually happened.
4. A research agent uses memory without confusing it with evidence
Long-term memory says the reader prefers short definitions before technical detail. That preference shapes presentation. The current workflow state records the research question, candidate sources, verification status, unresolved claims, and completion criteria. Retrieved documents enter model context as untrusted evidence with citations. The final article cites authoritative sources rather than citing memory.
If memory contains “Company X supports feature Y,” the agent treats it as a lead, not a fact. It verifies the live official documentation because product features can change. Memory reduces repeated work, but it does not replace freshness checks.
Choosing an Architecture Without Overbuilding
A simple chat assistant may need only server-managed conversation continuity and a small profile store. A tool-using assistant that can modify records needs structured task state, permissions, effect tracking, and audit evidence. A long-running workflow needs durable checkpoints, concurrency control, schema migration, and tested recovery. Architecture should follow effect and lifetime, not fashion.
| Agent pattern | Minimum state approach | Add when risk grows |
|---|---|---|
| Read-only question answering | Selected model context and session continuity | Source freshness, memory controls, citation evidence |
| Personal assistant | Session history plus scoped preference memory | Consent, deletion, tenant isolation, current-source checks |
| Tool-using transactional agent | Structured workflow state and stable operation keys | Approval records, effect ledger, independent audit |
| Long-running workflow | Durable state and semantic checkpoints | Leases, versioning, migrations, reconciliation, recovery tests |
| Multi-agent system | Shared task identity and typed handoff state | Owner per item, authority delegation, lineage, conflict control |
The site's AI agent state machine guide explains how explicit states and guarded transitions make tool workflows predictable. The AI agent controls explainer covers tools, permissions, memory, and human approval. This article supplies the conceptual map connecting those implementation pieces.
Be cautious with a single vector database marketed as universal memory. Vector search is useful for retrieving semantically related material, but it is not a transaction coordinator, authorization system, checkpoint engine, or immutable audit log. Similarity does not guarantee freshness, correctness, scope, or permission. Use retrieval where approximate relevance is appropriate and structured systems where exact current state matters.
Limits and Misconceptions
“A larger context window solves state”
A larger window can preserve more information for a model call. It does not create durable recovery, prevent concurrent writes, authenticate session access, verify external effects, or enforce retention. Context capacity and state correctness are different properties.
“The model can summarize its own state”
A model can create a useful summary, but the summary is an interpretation. It may omit a constraint, compress two statuses into one, or describe an intended action as completed. Preserve authoritative structured fields and raw evidence beneath the summary.
“Memory makes an agent autonomous”
Memory can improve continuity and personalization. Autonomy also depends on tools, permissions, planning, monitoring, recovery, and human decision rights. More memory can increase risk when stale or poisoned information persists.
“Checkpointing means exactly-once execution”
A checkpoint supports restoration. Exactly-once external effects are rarely guaranteed by snapshotting alone. Use idempotency keys, intent records, transactions where available, and reconciliation against the external system.
“Audit logs and checkpoints are interchangeable”
A checkpoint is optimized for continuation. An audit log is optimized for evidence and accountability. A checkpoint may be overwritten or pruned. An audit record may be immutable but insufficient to reconstruct every runtime object. Design both for their purpose.
State design cannot make an open-ended agent perfectly predictable. The model may misunderstand a goal, a policy may be wrong, or the environment may change. Good state architecture narrows ambiguity, protects authority, makes failures recoverable, and creates evidence. It turns hidden continuity into an explicit system property.
FAQ About AI Agent State
What is AI agent state?
AI agent state is the structured information that represents the current condition of an agent task, including identity, progress, decisions, approvals, tool results, confirmed effects, pending actions, and recovery metadata. It lets the surrounding system determine the next valid transition.
Is AI agent state the same as memory?
No. State usually describes what is true for a current execution. Memory retains selected information for later recall across turns or tasks. Some frameworks use the word memory broadly, but the design distinction remains useful because current progress and reusable knowledge need different controls.
What is the difference between context and state?
Context is the information made available to the model for a particular call. State is the broader condition maintained by the application or workflow. The runtime renders relevant state into context, while keeping permissions, secrets, and exact operational fields in controlled systems.
What is a session in an AI agent?
A session is a continuity boundary that usually groups conversation history or related turns under an identifier. It can support memory within a conversation, but it is not automatically the same as a durable business task or workflow.
What should an agent checkpoint contain?
A checkpoint should contain enough versioned information to resume safely: task identity, schema version, current step, confirmed effects, pending work, approvals, relevant decisions, retry metadata, and references to external evidence. It should not blindly store unnecessary secrets.
Can a vector database store all agent state?
It can store and retrieve semantically related memory, but it is usually the wrong primary store for exact workflow status, transactions, authorization, concurrency control, or audit evidence. Use systems suited to each consistency and security requirement.
How do you prevent stale state?
Use versions, timestamps, ownership, expiry, authoritative source checks, optimistic concurrency, and reconciliation. Treat memories and summaries as leads when freshness matters. Do not let an old transcript override a current system of record.
Why do AI agents duplicate actions after restart?
The runtime may restore a state that does not include a completed external effect, especially when a tool response was lost. Prevent duplicates with intent records, stable idempotency keys, effect ledgers, and reconciliation against the external service before retrying.
How should multi-agent systems share state?
Share a stable task identity and typed handoff records with goals, inputs, constraints, authority, ownership, expected outputs, and expiry. Avoid using free-form summaries as the only shared state, and control concurrent updates with versions or leases.
The Core Idea
Reliable AI agents do not “remember everything.” They place the right information in the right layer. Model context supports the next inference. Conversation history supports continuity. Application context supports code. Workflow state supports correct transitions. Checkpoints support recovery. Long-term memory supports future relevance. Audit evidence supports accountability.
Once these roles are separated, many confusing failures become ordinary engineering problems. A lost constraint becomes a context-rendering problem. A repeated payment becomes an effect-tracking problem. An old preference becomes a memory-lifecycle problem. A broken resume becomes a checkpoint and reconciliation problem. A cross-user leak becomes an identity and authorization problem.
Sources were selected from current official OpenAI and Microsoft documentation. Community discussions informed reader questions but were not used as factual authority.

